Security
Secure Ways to Receive Sensitive Client Documents (2026)
Secure ways to receive sensitive documents from clients, compared. Why email and text are risky, what a safe setup looks like, and a checklist for any tool.
By Bibin MathewUpdated 18 min read
The short answer
The safest way to receive sensitive documents is a private upload link for each client that works over HTTPS, needs no account, limits access to your team and deletes the files automatically once you are done. Collect only what you need, move it into your system of record, and stop accepting IDs and statements by email or text.
If you collect driver's licenses, bank statements, pay stubs, tax slips or medical forms from clients, you are holding information that could cause real harm if it leaked. Most small businesses never decide to be careless with it. They just use whatever is in front of them: email, text messages and a shared folder. A year later, those tools have turned into a pile of IDs and account numbers spread across inboxes, phones and old links nobody remembers sharing.
This guide is for owners and teams who receive sensitive documents as part of everyday work: property managers, accountants, mortgage brokers, law firms, insurance contractors, HR and staffing teams. You'll get a plain comparison of the common methods (including where the simple ones are perfectly fine), the principles behind a safer setup, a checklist to evaluate any tool, copy-ready wording for clients, and a step-by-step walkthrough of how to do it in Tangentflow.
What counts as a sensitive document
A document is sensitive when someone could use it to impersonate your client, open accounts in their name, or learn something private they never meant to share widely. In practice, that covers more than most people expect.
| Document | Why it's sensitive | Do you need the full copy? |
|---|---|---|
| Driver's license, passport, ID card | Name, date of birth, ID number, photo | Often yes, but rarely for long |
| Bank statements | Account numbers, balances, spending | Often only the summary page |
| Pay stubs and W-2s or T4s | Employer, income, SSN or SIN | Usually yes for lending and tax |
| Tax returns and slips (1099, T5) | Full financial picture, SSN or SIN | Yes for tax work |
| Medical or insurance records | Health details | Only the relevant pages |
| Voided checks, direct deposit forms | Routing and account numbers | Yes, for payroll setup |
| Signed contracts and applications | Signatures, personal details | Yes |
The right-hand column matters. A lot of risk comes from collecting more than the job needs, then keeping it forever. We'll come back to that under data minimization.
Why email attachments, texts and shared folders are risky
Email and text are convenient, which is exactly why they are the default. But they were never designed to move and store sensitive documents.
Email attachments
- Copies multiply. One attachment ends up in the client's sent folder, your inbox, every colleague you forward it to, and every phone and laptop that syncs those accounts.
- Files stay forever. Few people delete old attachments. A license sent three years ago is still sitting in a thread.
- Mistakes are easy. Autocomplete sends the file to the wrong "Sarah." A reply-all includes someone who should never see it.
- One breached inbox exposes everything. If an email account is compromised, every attachment in it is exposed at once. Shared mailboxes make this worse.
- Protection in transit is inconsistent. Whether an email is encrypted between servers depends on both providers, and neither you nor your client can easily tell.
Text messages
- Photos live on personal phones. Staff phones end up holding client IDs next to family photos.
- Backups copy everything. Phone backups can sync texted images to personal cloud accounts you don't control.
- Hard to organize or delete. There is no clean way to file a texted bank statement with the rest of a client's documents, or to be sure every copy is gone.
Shared cloud folders
Shared Google Drive or Dropbox folders are better organized, but they bring their own risks: links set to "anyone with the link," folders that are never closed, clients seeing each other's files when a permission is set wrong, and no automatic cleanup when the job ends.
Six ways to receive sensitive documents, compared
There is no single right answer for every business. Here is an honest comparison of the six methods most small businesses use.
| Method | Client effort | Cost | Security | Auto-deletion | Reminders |
|---|---|---|---|---|---|
| Plain email attachments | Low | Free | Weak | No | Manual |
| Encrypted or secure email | Medium | Often included | Good in transit | Rarely | Manual |
| Shared Drive or Dropbox folder | Medium | Low | Depends on settings | No | Manual |
| Client portal (practice software) | High (account, password) | $ per seat | Good | Varies | Some |
| File request links (Dropbox, Box) | Low | Low | Good | No | No |
| Private upload link per request | Low (no account) | Free to low | Good | Yes, if built in | Yes, with an agent |
When the simple options are fine
Being honest about this saves you money:
- Plain email is fine for non-sensitive paperwork: a signed quote, a floor plan, a photo of a damaged fence. The risk comes from IDs, statements and tax documents.
- Encrypted email (Microsoft 365 message encryption, Gmail's confidential mode or a secure mail add-on) is reasonable when you only need one document now and then from a client who is comfortable with it. It still leaves copies in inboxes.
- A shared folder works well for long-running relationships, like a bookkeeping client who drops receipts every month, as long as each client has their own folder, sharing is limited to their email, and you clean it out on a schedule.
- A client portal makes sense if you already pay for practice management software and your clients log in for other reasons. The trouble is that many clients forget their password and fall back to email.
- File request links from Dropbox or Box are a solid free option for occasional uploads. They don't tell the client what you need, check what arrives or chase anyone.
The private upload link shines when you collect a set of documents from many clients, need them to be right the first time, and want them gone afterward.
What a secure setup looks like
A safer process rests on a few principles. None of them require a big IT budget.
| Principle | What it means in practice |
|---|---|
| Private links | Each client gets their own link that only opens their request |
| Encryption | Uploads travel over HTTPS and are encrypted at rest |
| No client accounts | Nothing to forget, reset or phish |
| Access control | Only the right people on your team can see files |
| Automatic deletion | Files are removed once you no longer need them |
| Data minimization | You collect only what the job requires |
| One destination | Files end up in one place, not five |
Private, per-client links
A private link for each request means one person's documents are never mixed with another's. The link should be unguessable and tied to a single request. Ideally the client doesn't need an account, because password resets and forgotten logins push people straight back to email.
Encryption in transit and at rest
Uploads should happen over HTTPS (the padlock in the browser), which protects the file on its way from the client's phone to the service. Ask any vendor how files are protected at rest too, and where they are stored.
Access control on your side
Decide who on your team really needs to see client documents. Avoid a single shared login. When someone leaves, remove their access the same day.
Automatic deletion
This is the principle most businesses skip, and it may matter most. A file you have deleted cannot be exposed in a breach. Once the job is done and you've moved what you need into your system of record, the copies in your collection tool should disappear on their own, not when someone remembers.
Emails clients can trust
Phishing works because clients are used to receiving "please upload your documents" emails. A trustworthy request comes from your business name, explains why the client got it, and says clearly what you will never ask for, such as passwords, PINs or card details.
Collect less: data minimization in practice
The cheapest security upgrade is collecting less. A few examples:
- Only need a name and address? Ask for a utility bill, not a full bank statement.
- Only need proof of income? Ask for the most recent two pay stubs, not three months of bank activity.
- Tell clients they can black out account numbers except the last four digits when you don't need them.
- Ask a yes or no question first. "Do you have rental income?" before requesting rental statements, so only the clients who need to send them do.
- Decide whether IDs should go through automated tools at all. Many businesses prefer that government IDs are stored and reviewed by a person only. Choose a tool that lets you exclude them.
- Set a short retention period. If you only need a document to make a decision, there is no reason to keep the copy for a year.
A checklist for evaluating any tool
Use this to review your current process or a new tool, including the one you already pay for.
- Each client gets a private link to their own request only
- Clients do not need to create an account or remember a password
- All pages and uploads use HTTPS
- Files are encrypted at rest by a provider that explains how
- Only authorized staff can see client files, each with their own login
- Files are deleted automatically after a set period or when the job is done
- You can delete a request immediately, and you get a record that it was deleted
- You can exclude specific items, such as IDs, from AI or automated processing
- Request emails come from your business name and warn against phishing
- There is one place where all of a client's files end up
- Clients are told clearly what you need and why
- Your team knows not to accept sensitive documents by text
If your current setup misses three or more of these, it's worth changing.
How to receive sensitive documents securely in Tangentflow
Tangentflow is built around the principles above: one private link per request, no client accounts, every upload checked, and files deleted when you're done. Here is how to set up a secure request from start to finish.
Step 1. Build a checklist of exactly what you need
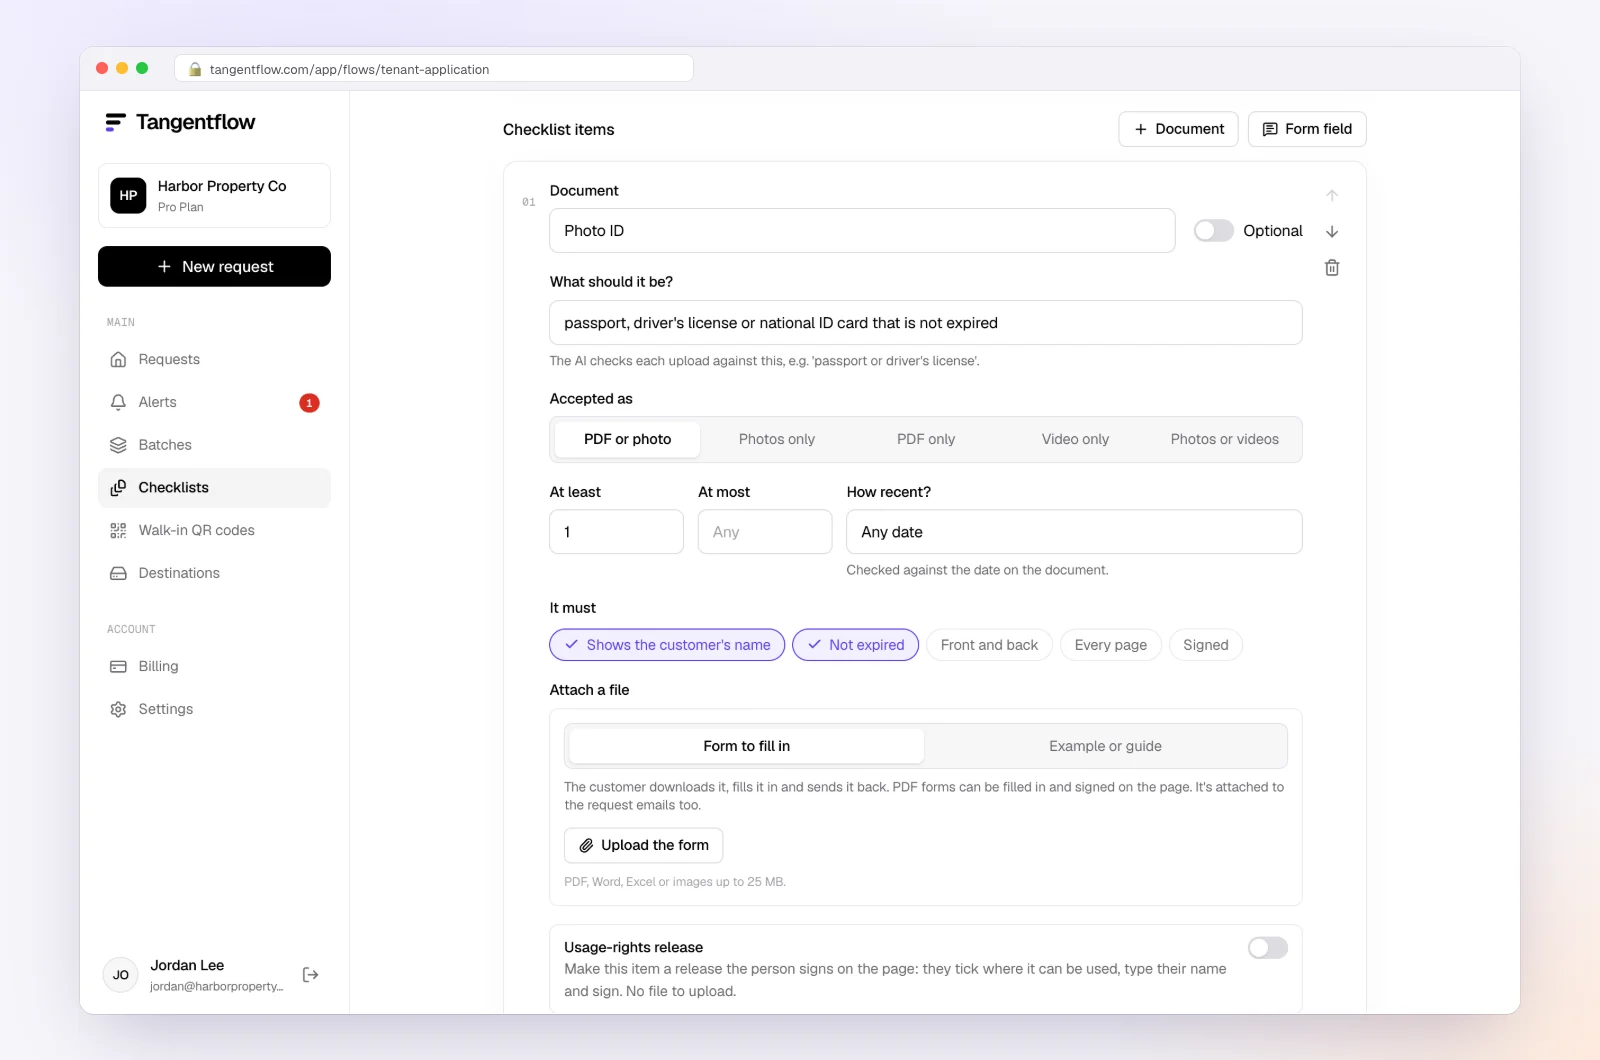
Go to Checklists and choose Browse templates (for example "Client ID check (AML / KYC)", "Mortgage application pack" or "Year-end documents"), describe what you need and let AI draft it, or choose Add your own items one by one.
For each item, fill in "What should it be?" so the check knows what to expect, set a count, and add a date rule like "dated in the last 3 months" or "not expired" where it applies. This is also where you practice data minimization: mark items optional, and use "Only ask if…" so a document is only requested when an earlier yes or no answer calls for it.
Step 2. Keep the most sensitive items out of AI checks
For items like a passport or driver's license, you can switch the AI check off on that item (or for the whole checklist). Those files are never sent to the AI provider. They are stored and marked "Received" for a person on your team to review. For items you do check, full ID, account and card numbers are never kept in summaries, only the last four characters.
Step 3. Create the request
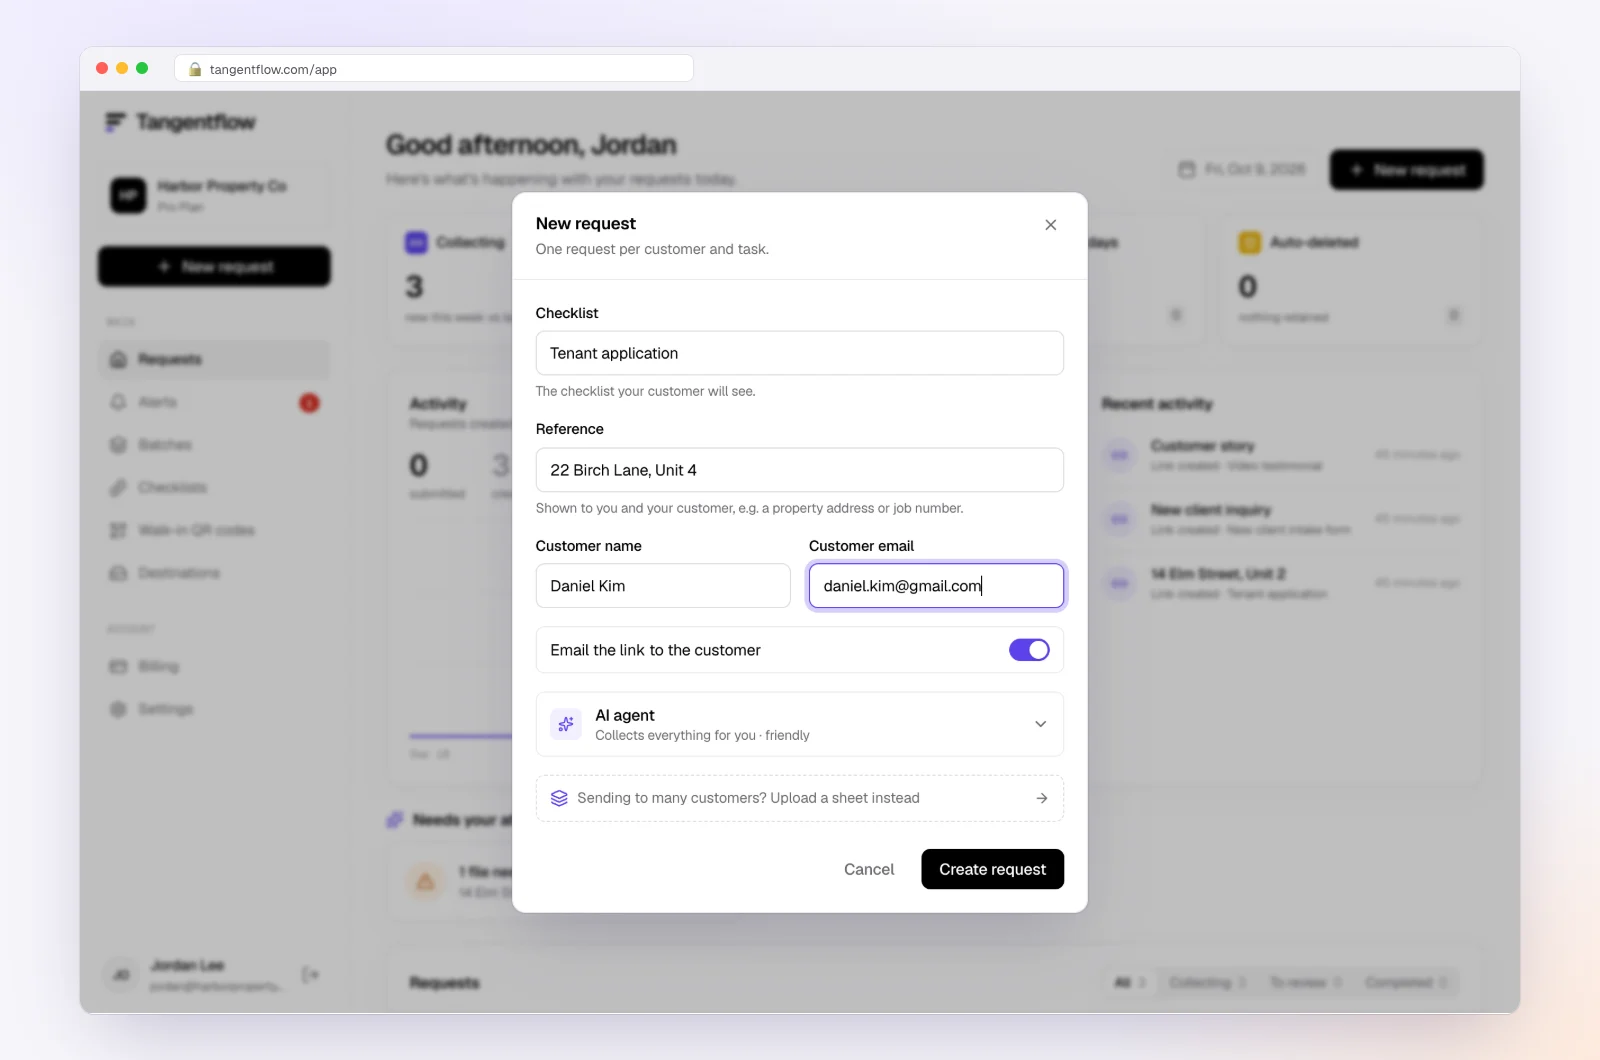
Open Requests and click New request. Pick the checklist, add a reference (like "Ortiz refinance" or "14 Elm Street, Unit 2"), the client's name and email, and a needed-by date. Leave "Email the link" on to have the AI agent send the invitation, or turn it off and copy the link to share yourself.
Step 4. The client uploads from their phone
The client gets an email from your business name via Tangentflow with a button to their private link. No account, no app, no password. The page shows exactly what's needed and what's still missing, and every upload travels over HTTPS.
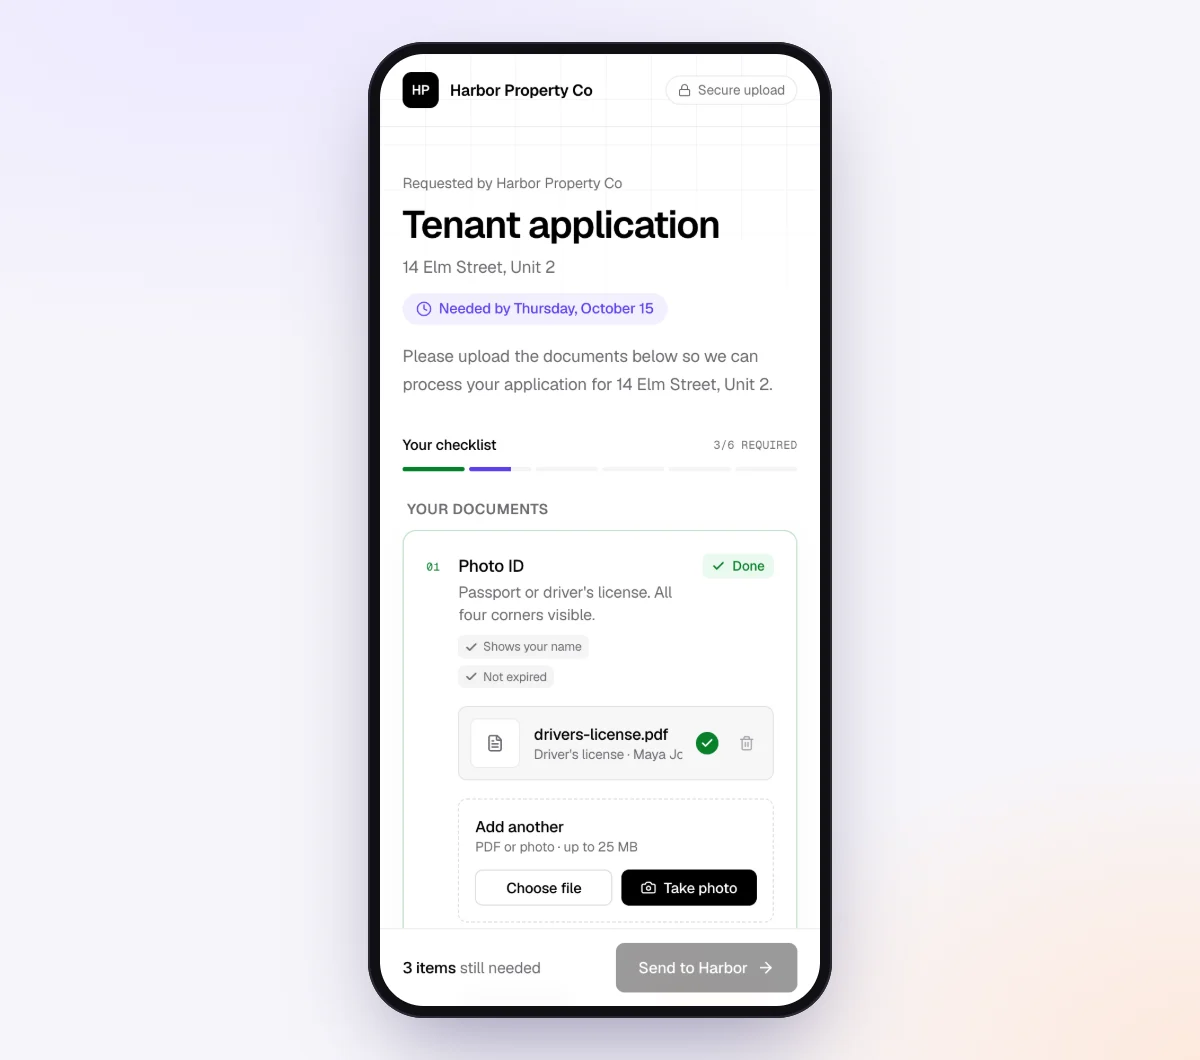
Each file is checked in seconds for the right document type, readability, dates and conditions like the client's own name or front and back. If something is wrong, the client sees a friendly note and can fix it before leaving the page, which means fewer follow-up emails asking for a better copy. Learn more about instant document checks.
Step 5. Review, deliver and let it disappear
On the request page you'll see every file with its check result, what's still missing and an activity timeline. Download the organized ZIP package, or deliver to Google Drive or your own system by webhook on Pro. Then mark the request complete.
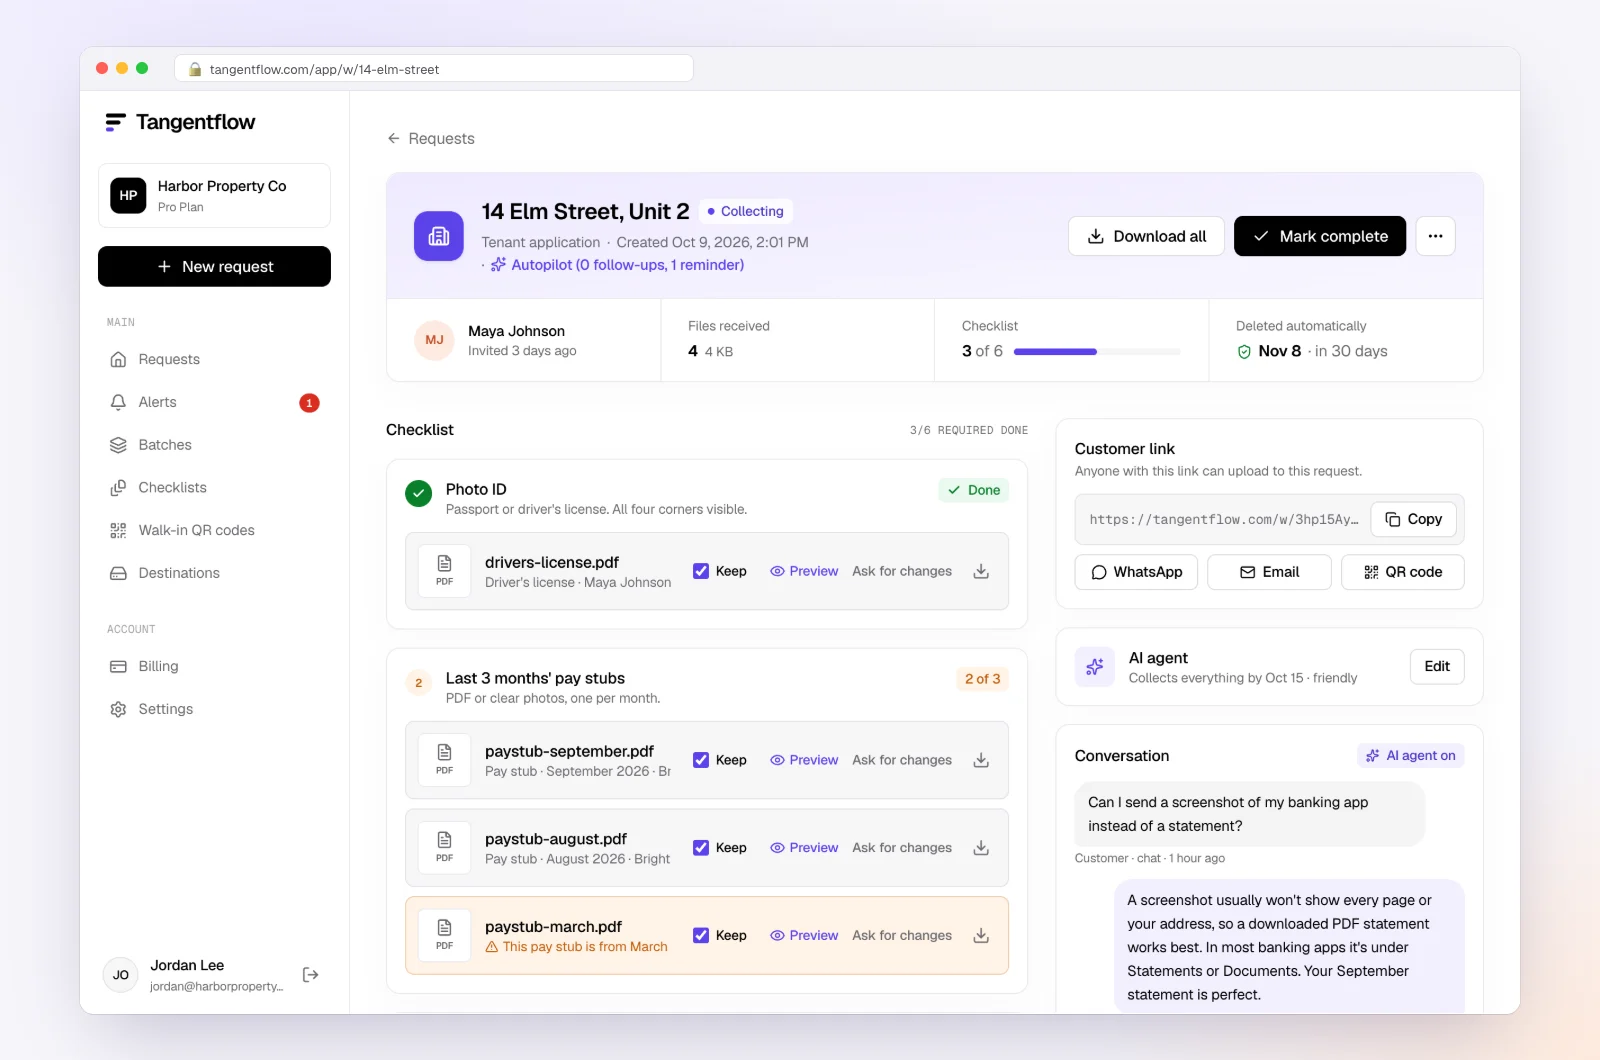
What happens after: retention, deletion and delivery
The part most tools leave to you is built into Tangentflow:
- Deleted 24 hours after you complete a request, or when the retention period ends: 7 days on Free, 60 days on Pro.
- Delete now at any time from the request page. Each deletion is recorded with a deletion certificate.
- Keep longer or hold lets you move the deletion date within your plan's limit, or put a request on hold with a short reason (for example, during a dispute).
- No permanent repository. Tangentflow is not where documents live. Download or deliver them to your system of record, then let the copy disappear.
- Encrypted at rest on Cloudflare's infrastructure, reachable only through your signed-in account or the client's own link.
- Email replies are accepted only from the client's address on file, through a private reply address for that request.
More detail is on the security page.
Setups for every kind of business
Here are starting points for common situations. Each one keeps sensitive items tight and the retention short.
| Business | Checklist items | Settings | Learn more |
|---|---|---|---|
| Property manager | Photo ID, two pay stubs, prior landlord reference | ID with AI check off, pay stubs dated last 60 days | Property management |
| Accountant or tax preparer | W-2s or T4s, 1099s or T5s, last year's return | "Only ask if" for rental and business income | Accounting and tax |
| Mortgage broker | ID, pay stubs, bank statements, employment letter | Statements "dated in the last 3 months", every page | Mortgage lending |
| Law firm | Photo ID, proof of address, signed retainer | "Client ID check" template, deliver to your storage | Law firms |
| HR and staffing | ID, tax form (W-4 or TD1), direct deposit form | ID with AI check off, form attached to item | Staffing and onboarding |
| Restoration contractor | Insurance policy, claim letter, signed authorization | Signed, every page | Insurance restoration |
For a deeper look at what to request in each case, see the rental application documents checklist and the client tax document checklist.
Telling clients how to send documents
Clients default to email or text unless you give them an easier option. Make the secure path the obvious one, and say why. Put a version of this in your first request:
Subject: Your documents for [reference], secure upload link inside

Hi [First name],

To get started on [job], we need a few documents from you. To protect
your information, please don't email or text them. Instead, upload them
using your private link:

[link]

It works on your phone, you don't need an account, and it shows exactly
what we need. Files are deleted automatically once we're done with them.

We will never ask for your passwords, PINs or card details.

Thanks,
[Your name]
[Business name]
And when someone emails a sensitive file anyway:
Hi [First name],

Thanks for sending this. For your security, we've moved it to your
private file and deleted the email. For anything else, please use your
secure link instead of email: [link]

[Your name]
For the full workflow beyond security, read our guide to collecting documents from clients. Our document request email templates have more wording you can adapt, and the client reminder schedule covers how often to follow up without being pushy.
What to do with documents that already arrived by email
If clients still email documents, have a simple weekly routine:
- Move the file into your system of record or secure collection tool.
- Delete the email and attachment from your inbox and your sent folder, then empty the trash.
- Check that the file isn't also sitting in a downloads folder on your computer.
- Reply with the secure link for future documents.
On Pro, clients can also reply to the Tangentflow email with attachments. Those files are checked and filed under the right checklist item, so they don't sit scattered across a thread in your own inbox.
When something goes wrong
| Problem | What to do |
|---|---|
| Client sent an ID by text anyway | Save it to the request, delete the text and any photo on the staff phone, reply with the link |
| Client says the email looks like phishing | Confirm by phone, point them to your business name and the "we never ask for passwords" line |
| Client can't find the email | Copy the link from the request, or show a QR code with "Show full screen" in person |
| Wrong person received a link | Delete the request right away, which stops the link working, and create a new one |
| Upload was flagged but the document is correct | Review it yourself on the request page; the AI check helps, you decide |
| You need a file after it was deleted | It's gone by design. Ask the client again, and next time use "Keep longer or hold" |
| A staff member left | Remove their access the same day and review what they could see |
Free and Pro
You can set up a secure request today without paying anything.
| Free | Pro ($29/month) | |
|---|---|---|
| Open requests | 1 at a time | Unlimited |
| AI check on each file | Yes | Yes |
| AI autopilot (invites, answers, reminders, follow-ups) | Your first request | Every request |
| Files kept | Deleted after 7 days | Up to 60 days |
| Clients reply by email with attachments | No | Yes |
| Delivery to Google Drive or a webhook | No | Yes |
| Branding | Tangentflow badge | Your logo |
Both plans include unlimited checklists, QR codes and posters, ZIP export, AI summaries and email delivery. Pro is monthly, cancel any time, no contract. See pricing for details.
The whole process as a checklist
- List the documents you actually need, and drop anything you don't.
- Decide how long you need each one and set a short retention.
- Build a checklist with clear "What should it be?" descriptions and date rules.
- Switch the AI check off for items like government IDs if you prefer human review only.
- Create one request per client with a reference and a needed-by date.
- Send the private link from your business name, with a line telling clients not to email or text documents.
- Let the agent remind clients about only what's still missing.
- Review files on the request page and ask for changes where needed.
- Download or deliver the package to your system of record.
- Mark the request complete and let the files delete themselves.
- Clean emailed and texted documents out of inboxes and phones weekly.
Frequently asked questions
Is it safe to receive documents by email?
Email is fine for everyday paperwork, but it's a poor fit for IDs, statements and tax documents. Attachments multiply across inboxes and devices, often stay forever and are all exposed if one account is compromised. A private upload link with automatic deletion is a safer choice.
What is the most secure way for clients to send documents?
A private upload link for each request, over HTTPS, with no client account to break into, access limited to your team, and automatic deletion once you're done. Pair it with collecting only what you need.
Should I accept ID photos by text message?
It's best to avoid it. Texted photos stay on personal phones and backups and are hard to file or delete reliably. Point clients to a secure upload link instead, and delete any texted copies once they're saved.
How long should I keep client documents?
Only as long as you need them for the job and any retention rules that apply to your profession. Keep the official copy in your system of record, and let collection tools delete their copies automatically. Check with your regulator, CPA or lawyer for specific periods.
Does Tangentflow verify that an ID is real?
No. The AI check confirms the upload looks like the right document, is readable, isn't expired and shows the client's name. It is not identity verification. If you need to confirm identity, use a dedicated verification service or check the ID yourself.
Are files sent to an AI provider?
Only for items with the AI check on. You can switch it off for a whole checklist or for single items like IDs, and those files are never sent to the AI provider. Full ID, account and card numbers are never kept in summaries.
Is Tangentflow HIPAA compliant or SOC 2 certified?
No, it doesn't hold those certifications today. If your work requires them, use a tool that does. For everyday sensitive documents like pay stubs, IDs and tax slips, Tangentflow's private links, encryption and automatic deletion cover the principles in this guide.
Can clients upload without creating an account?
Yes. Each client opens their private link in any phone or computer browser and uploads directly. There's no account, password or app, which also means there's no client login to phish.
Should clients password-protect PDFs before emailing them?
It helps if an attachment goes to the wrong place, but only when the password goes by a separate channel. Clients often forget the password or reuse a weak one. A private upload link avoids the problem, and in Tangentflow you can turn on "Require an email code" so the link only opens after the client enters a 6-digit code sent to their email.